Key Takeaways
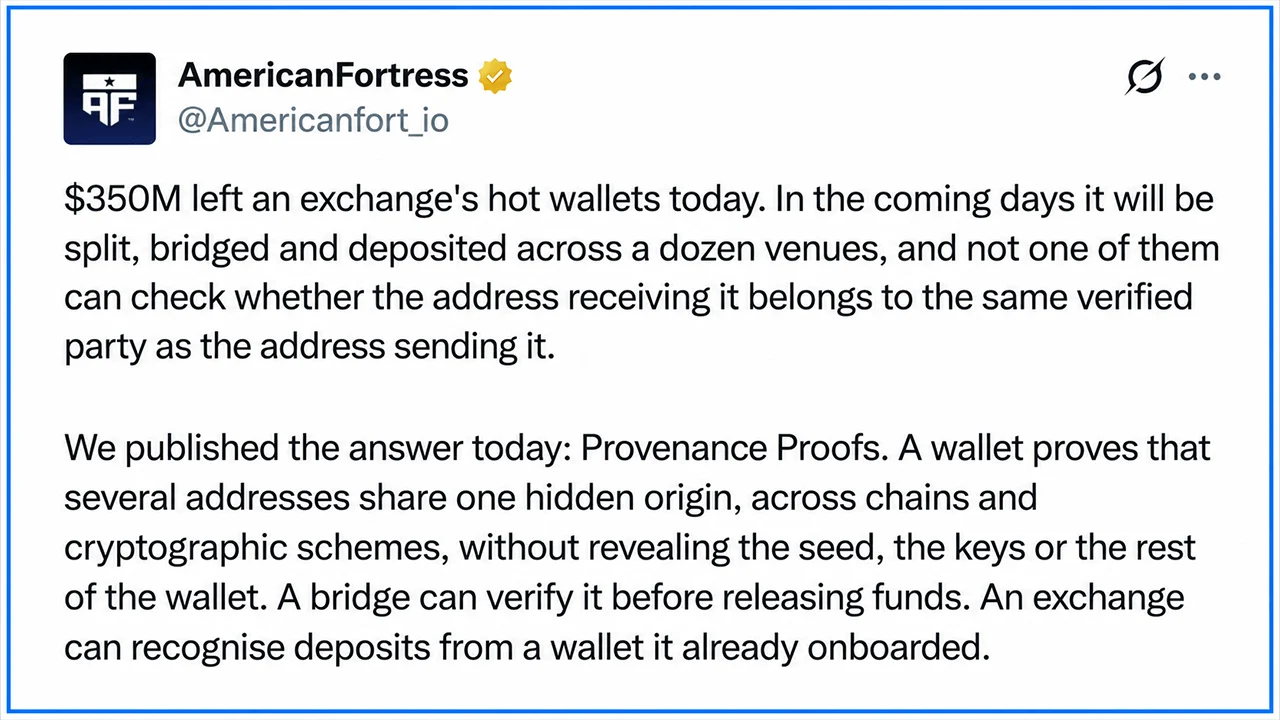
- Americanfortress introduced ZK-POSP to link 1 wallet’s keys without exposing seed phrases.
- CEO Michal Pospieszalski noted ZK-POSP makes bridge hacks non-viable by requiring 1:1 user funds.
- An SDK integration into Metamask will process 1 automated proof in 3 seconds for users.
Solving Blockchain’s Multi-Key Privacy Dilemma
Researchers at cryptography firm Americanfortress have unveiled a cryptographic technique that solves one of blockchain’s most persistent dilemmas: how to prove that multiple cryptocurrency addresses, identity keys, or compliance badges belong to the same wallet without giving away private seed phrases or exposing financial history to the public.
The breakthrough, detailed in a research paper released on Sept. 24, expands on zero-knowledge (ZK) cryptography. While existing ZK tools can prove that a single address was created legitimately from a real wallet, real-world finance often requires showing relationships between multiple keys. Until now, proving these connections meant either revealing secret recovery phrases or exposing every address in the wallet.
To tackle this, researchers Vincenzo Botta, Michal Pospieszalski, Emanuele Ragnoli, and Justus Ranvier created three flexible disclosure options, giving users control over how much information they reveal.
Defending Against Exploits and Address Hijacking
When asked how the ZK-POSP framework alters the landscape for attackers relying on address hijacking or spoofing, Americanfortress CEO Michal Pospieszalski emphasized the protocol’s impact on decentralized finance (DeFi).
“When ZK-POSP is built into a DeFi protocol, every transaction must pass an extra security check before processing,” Pospieszalski said. “Whichever party initiates the transaction must prove that the source of funds and the destination address belong to the same entity. That makes stealing from a cross-chain bridge significantly harder. To bypass the verification step, an attacker would first need to commit an equal amount of their own capital and initiate a legitimate transaction. At that point, exploiting the bridge becomes economically unviable.”
Despite the complex cryptography operating under the hood, Pospieszalski noted that day-to-day user experience will remain uninterrupted.
“We are integrating our software development kit (SDK) into MetaMask, which generates the required proofs automatically,” Pospieszalski explained. “Users will see a status notification in the interface indicating that a proof is being generated. The process takes roughly three seconds, so we do not expect it to create friction.”
He added that a DeFi-side oracle verifies the proof before finalizing the transaction. If verification fails, funds automatically return to the source address, giving users a visible extra security step that builds confidence without adding complexity.
Granular Privacy for Audits and Compliance
The framework also addresses compliance hurdles, such as generating proof of payment origin for auditors without leaking metadata or enabling off-chain transaction graph reconstruction.
“To demonstrate wallet activity to a third party, a user generates a zero-knowledge proof tied specifically to the individual on-chain transaction,” Pospieszalski told Bitcoin.com News. “For example, if Bob needs to prove he received funds from Alice from a designated address, the proof enables the verifier to validate that exact address on-chain. While the proof confirms the specific address involved to that sole counterparty, it also proves ownership by the sender without exposing unassociated wallet history.”
Because only transaction-specific data already present on the public ledger is disclosed, external auditors cannot reconstruct broader off-chain transaction graphs.
Practical Applications and Post-Quantum Readiness
Beyond audits and DeFi bridges, the research team outlined several immediate uses for the technology across everyday crypto interactions, including address books to verify that a fresh payment address belongs to a verified recipient before funds are sent. The technology also enables crypto exchanges to verify anti-money laundering (AML) status on incoming deposits while preserving user anonymity.
If users rotate their security keys after a breach, the system proves continuity, verifying that new keys inherit the history of old ones without compromising safety. Furthermore, the proofs are designed to work alongside post-quantum cryptographic standards, ensuring long-term security against future quantum computing threats.
By enabling precise control over privacy and verification, the framework aims to bridge the gap between regulatory requirements and personal financial privacy on public blockchains.