Key Takeaways
- Bloom Trading confirmed that an Oct. 26 exploit drained 9,408 SOL worth approximately $947,000.
- Bloom identified a third-party RCE vulnerability and said no private keys were compromised.
- Bloom pledged full reimbursement to nine affected users controlling 49 wallet addresses.
Hacker Drains 9,408 SOL Through Third-Party Vulnerability
Bloom, a Telegram-based cryptocurrency trading bot supporting Solana and Ethereum Virtual Machine (EVM) networks, suffered a security breach on Oct. 26, 2026, that resulted in approximately 9,408 SOL disappearing from users’ wallets.
The stolen cryptocurrency was valued at approximately $947,000, according to Bloom’s official investigation, although early blockchain parsing estimates placed the damage closer to $954,000.
Blockchain monitoring account Onchain Lens flagged the suspicious transfers, while Onchain Alert reported that the attacker consolidated stolen funds into a suspected drainer wallet. Onchain Alert warned on X:
“A hacker drained 9,408 SOL from 49 victims in one of its drainer [wallets], final number might be much higher.”
The monitoring account identified the largest individual drain as 1,636 SOL, worth approximately $166,000. Early reports suggested the attacker primarily targeted SOL holdings while leaving some USDC stablecoin balances untouched.
Bloom Confirms Nine Victims and Rules Out Private-Key Theft
The initial reports suggested 49 separate victims. Bloom’s subsequent investigation narrowed that figure to nine users controlling 49 affected wallet addresses. The company identified a complex remote code execution (RCE) vulnerability involving a third-party software module as the attack’s entry point.
“No private keys were compromised, unaffected wallets are safe, and all affected users will be fully reimbursed by Bloom.”
That distinction matters because an RCE exploit can potentially let an attacker manipulate a compromised software environment without directly extracting users’ private keys. However, Bloom hasn’t publicly disclosed the precise mechanism used to authorize the unauthorized transfers.
The company temporarily disabled services as a precaution and directed affected customers toward its support channels.
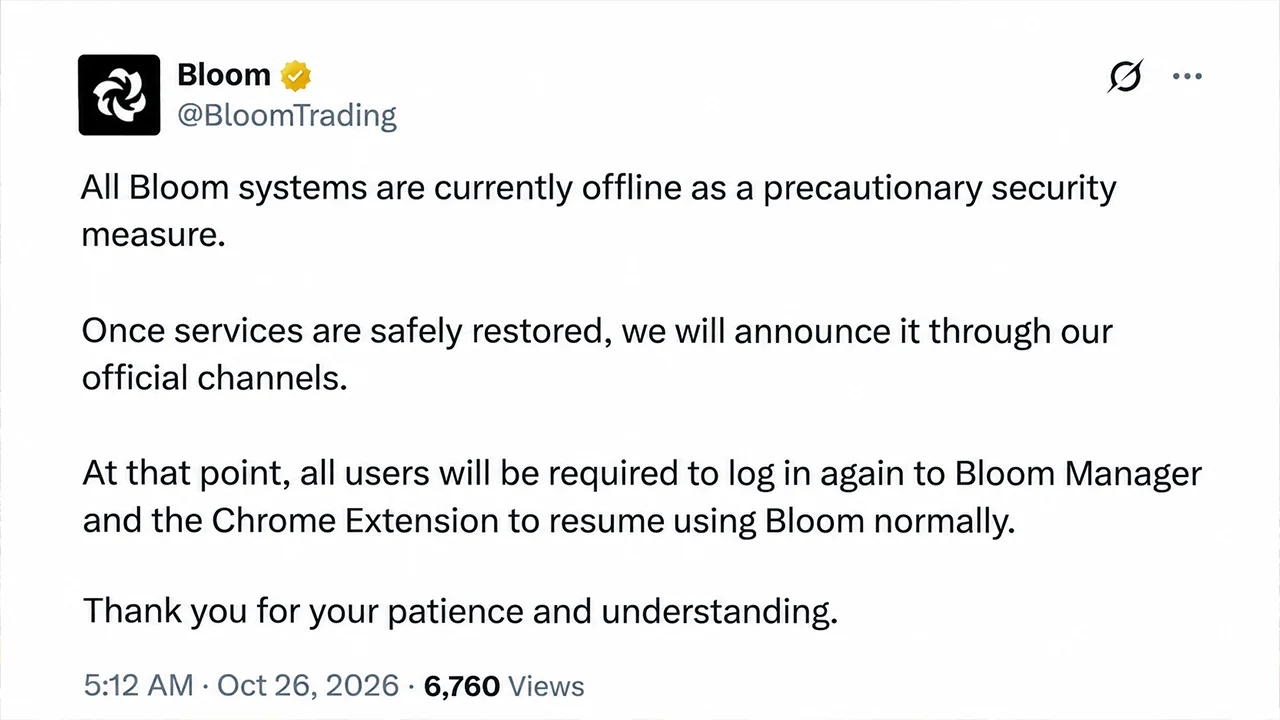
“All Bloom systems are currently offline as a precautionary security measure. Once services are safely restored, we will announce it through our official channels. At that point, all users will be required to log in again to Bloom Manager and the Chrome Extension to resume using Bloom normally. Thank you for your patience and understanding,” the team’s X account said.
Bloom Promises 100% Reimbursement as Investigation Continues
Rather than leaving customers to absorb the damage, Bloom pledged to foot the entire bill. The company stated:
“Bloom will fully reimburse 100% of the stolen funds directly to secure wallets designated by the affected users.”
Bloom insisted it is also tracing the stolen cryptocurrency, exploring freezing and recovery options, and attempting to identify the attacker. Its statement emphasized that the team has developed software since 2018 and operated in cryptocurrency markets since 2021. Affected customers have been advised to transfer remaining assets into newly generated wallets.
Bloom has not publicly established a reimbursement deadline or announced when normal operations will resume. The news comes as a growing array of system bugs, data breaches, and hacks have taken place across the crypto industry, with many pointing the finger at artificial intelligence (AI) assistance.
This particular breach leaves an uncomfortable technical question hanging over trading bots that manage customer wallets. If private keys remained secure, then precisely how did compromised third-party software gain the authority to move nearly $1 million?

