Key Takeaways
- Keystone disclosed an Oct. 24 breach exposing customer shipping information and purchase details.
- Keystone says private keys, recovery phrases and payment information were not compromised.
- Coldcard, Ledger, Trezor and Safepal also faced major security incidents in 2026.
Keystone Customer Data Breach Exposes Buyers to Targeted Scams
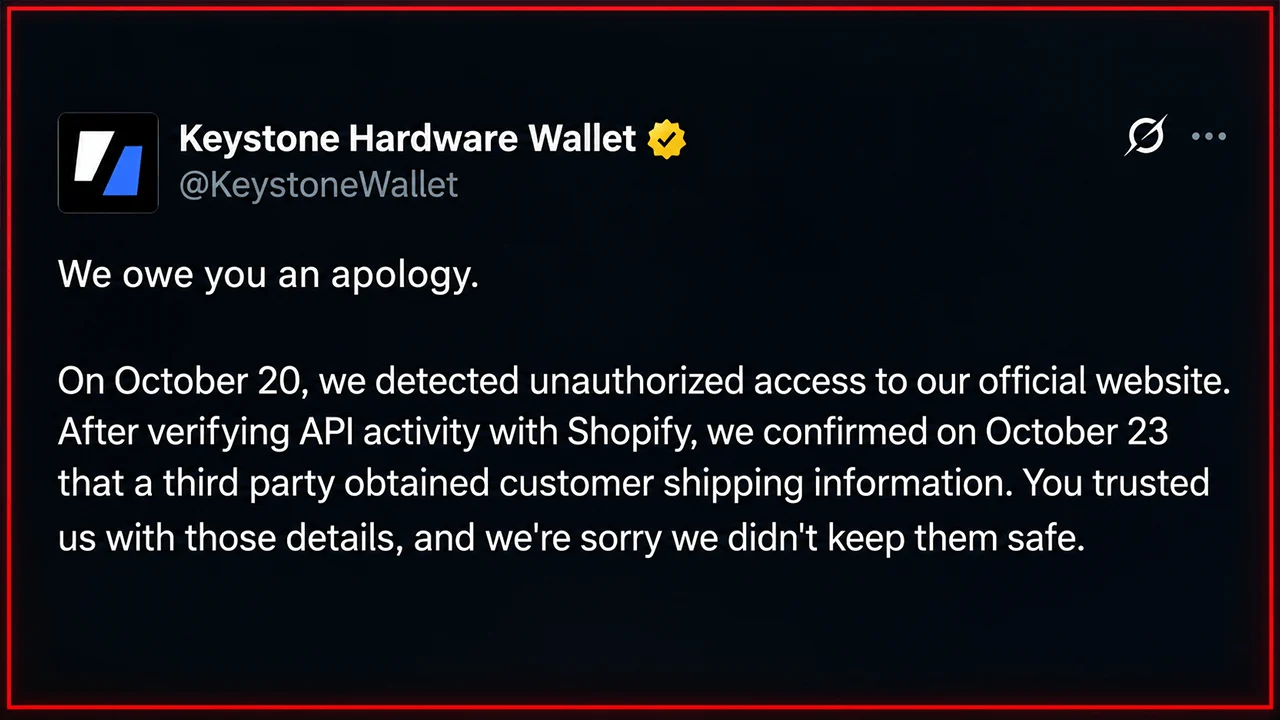
A hardware wallet designed to keep cryptocurrency secrets offline has encountered a security problem somewhere entirely different: its online storefront. On Saturday, Keystone disclosed at 1:59 p.m. ET that an unauthorized party had obtained customer shipping information through its website, potentially giving scammers the personal details needed to impersonate the company.
Keystone insists that recovery phrases, private keys and payment information were not compromised, but the incident raises an uncomfortable question about how much protection an offline wallet provides when its owner’s identity and address are exposed.
Keystone Confirms Unauthorized Access
Keystone disclosed on X that it detected suspicious access Oct. 20 and subsequently examined application programming interface (API) activity with Shopify, its e-commerce provider. By Oct. 23, the company had confirmed that an unauthorized third party obtained customer names, contact information, shipping addresses, and purchase details.
The company says it blocked the intrusion, patched the vulnerability, and began notifying affected customers. However, Keystone has not disclosed how many buyers were exposed or precisely how the unauthorized access occurred.
Scammers Gain a Potential Opening
The immediate danger isn’t necessarily someone remotely emptying a hardware wallet. It’s someone using legitimate customer information to manufacture a convincing deception. Keystone warned customers about fraudulent refund offers, replacement devices, and unsolicited messages requesting sensitive information. The company emphasized that it never requests recovery phrases or private keys.
One X user wrote about the issue the day before Keystone confirmed the attack. “Just raising awareness here because I’m 99% convinced your customer database may have been leaked. I received a call from a spoofed Montreal SPVM number, and the guy tried to social-engineer me,” the X account OG Degen wrote. Customers should independently verify communications through Keystone’s official website rather than following unexpected links.
Hardware Wallet Security Takes Another Hit in 2026
Keystone’s disclosure follows a difficult year for hardware wallet manufacturers. Coldcard faced a massive bug with weak seed-generation randomness and substantial estimated losses, while Ledger confronted reports of tampered devices distributed through a reseller.
Trezor and Safepal also disclosed customer information breaches involving third-party fulfillment or ordering systems. Unlike incidents involving compromised recovery phrases, those exposures primarily created opportunities for phishing and impersonation.
For Keystone, the cryptographic defenses reportedly held. The troubling question is whether customers’ personal information received comparable protection.