Key Takeaways
- Bitget’s statement shared with Bitcoin.com News explains that the exchange traced its $388M breach to stolen credentials obtained through a third-party security flaw.
- Bitget processed 9,585 BTC withdrawals totaling 4,098 BTC by 9 a.m. UTC on Sept. 28.
- Bitget plans to restore ETH withdrawals Sept. 29 and release its security report this week.
Bitget’s $388M Breach Traced to Third-Party Security Flaw
Eight years without a security incident of this magnitude came to a screeching halt for Bitget on Sept. 24, when attackers exploited a vulnerability in a third-party security product and made off with approximately $388 million.
Four days later, according to a statement shared with Bitcoin.com News, the exchange is reopening its withdrawal gates, beginning with bitcoin. Bitget says its $464 million-plus User Protection Fund remains available to protect customers, while onchain investigators continue tracing the stolen assets. The latest disclosure also reveals a peculiar twist: The attackers didn’t need to steal private keys to pull off the heist.
In its Sept. 28 statement, attributed to CEO Gracy Chen, the exchange acknowledged the gravity of the incident, explaining that its previous security record was no excuse for what happened.
“The September 24 incident is the first time in eight years that an attack of this nature has breached Bitget Exchange’s infrastructure,” the company stated. “That record does not diminish the seriousness of the incident. It sets the standard against which Bitget’s response should now be measured.”
Stolen Credentials Let Attackers Bypass Wallet Safeguards
Bitget’s initial investigation found that the attackers obtained high-level internal credentials through a vulnerability in an external security product. Those credentials allowed them to issue fraudulent withdrawal commands to the exchange’s wallet system, circumventing existing risk controls.
Bitget explained:
“The investigation found that the attacker exploited a vulnerability in a third-party security product to obtain high-level internal credentials.”
The company added that those credentials enabled unauthorized transfers, while emphasizing that “private keys were not compromised and cold wallets were not affected.” The compromised infrastructure facilitated unauthorized transfers across multiple blockchain networks, including Ethereum, XRP Ledger, and Tron. Alongside this, platforms such as Thorchain and other rails like Uniswap, 1inch Fusion, and Stargate have been leveraged.
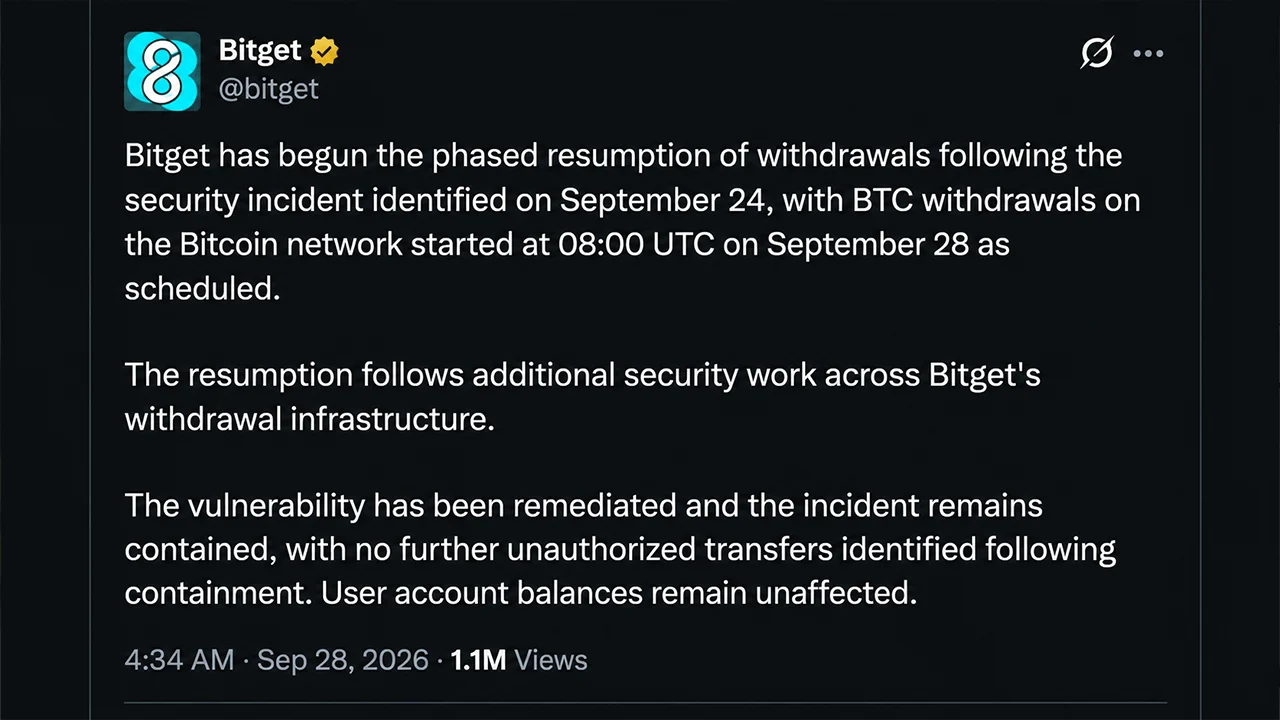
Bitget initially pegged the damage at $351.6 million before subsequent reconciliation raised the figure to approximately $388 million. Rather than cracking the cryptographic mechanisms protecting customer assets, the attackers exploited trusted access to the infrastructure responsible for authorizing withdrawals. “Bitget has identified the attack path, remediated the vulnerability, and strengthened controls across its withdrawal infrastructure,” the company explained on Monday.
The exchange is now reviewing its third-party security dependencies, internal access controls, withdrawal verification and abnormal activity detection. It maintains that customer account balances remain unaffected.
Bitcoin Withdrawals Return as Investigators Hunt Stolen Funds
Bitget said it began restoring BTC withdrawals across the Bitcoin and BSC networks at 8 a.m. UTC on Sept. 28. By 9 a.m., the exchange reported processing 9,585 BTC withdrawals totaling approximately 4,098 BTC. Regarding the updated loss estimate, the company clarified that it “does not represent additional unauthorized transfers following containment.”
Meanwhile, forensic specialists Mandiant and Slowmist are assisting with the investigation, examining the attack methods, validating remediation measures and tracking the missing cryptocurrency. “Some affected assets have already been frozen through coordination with industry partners,” Bitget disclosed on Monday.
The exchange has also shared identified attacker addresses and tracing information to help investigators follow the money. CEO Gracy Chen previously indicated that the attack methodology appeared highly consistent with North Korean-linked groups, although the investigation remains underway.
The company stated:
“Bitget expects to complete an official security report this week and will share further findings as they are verified.”
Bitget’s $464M Protection Fund Faces Its Biggest Test
The exchange’s statement reports a comprehensive reserve ratio of 127%, alongside a User Protection Fund exceeding $464 million. Its latest disclosure maintains that customer balances remain unaffected, despite the incident representing its first security breach of this nature in eight years.
“Bitget’s response to this incident will therefore extend beyond remediation of the vulnerability itself,” the company explained in the notice. ETH withdrawals are scheduled to resume Sept. 29, followed by USDT on Sept. 30 and other supported tokens, fiat and peer-to-peer services on Oct. 2.
“The focus now is on applying the findings from this incident across the platform and strengthening the safeguards required as Bitget’s infrastructure and product offerings continue to expand,” the statement shared with our newsdesk concludes.